Every service.
One gateway.
An all-in-one cloud networking platform that secures, transforms, and routes traffic to all your services no matter where they run.
Trusted by teams across the globe


Try ngrok by getting your service online.
Right now.
$ brew install ngrok$ scoop install ngrok$ docker pull ngrok/ngrokRead https://ngrok.com/agent-setup/prompt.md and follow it
to get my app online with ngrok.From localhost to live in prod.
Instead of a hodgepodge of nginx, NLBs, VPNs, model routers, and Cloudflare, solve every networking problem with one gateway.
Put your local app on a public URL
Deliver and secure APIs
Control devices in the field
Connect to APIs and DBs in customer networks
Don’t want services addressable
on the public internet?
Reach APIs, databases, and devices in private networks straight from your own cloud, cluster, or laptop—a VPN alternative with no firewall rules and no flat networks.
You may also need to…
Handle webhooks for production services
Assign secure URLs to previews and CI tests
SSH and RDP into devices in the field
Access remote K8s clusters from dev
Connect your local MCP server to ChatGPT and Claude
Replay HTTP requests to debug webhooks faster
Okay, but how does it work?
Connect anything with Endpoints, Traffic Policy, and Secure Tunnels.
Route, transform, and authenticate your traffic.
No more cryptic nginx configs or Lua plugins. Everything is a URL with traffic rules you attach. Compose them together and offload processing to ngrok’s cloud gateway.
Endpoints & Traffic Policy
Take action at any phase in the request lifecycle.
Traffic Policy is an expressive CEL-based rules system. When a request hits different phases of its lifecycle, ngrok executes each rule sequentially.
Even more ways to control and transform your traffic
Stop cobbling your infrastructure together.
Security, performance, and resiliency built in by default.
Turn one URL into a smart pool of replicas
Scale automatically by starting endpoints with the same URL. They self-register for load balancing. Stop them and they’re out.
Accelerate traffic with smart global routing
We reduce latency for your end users by routing every request across our global network to the nearest healthy replica.
Protect origins from DDoS with no extra work
ngrok automatically blocks volumetric attacks from malicious actors before any traffic reaches your network.
Serve HTTP, TLS, and TCP with native support
If it runs over TCP, it works on ngrok. Websockets, gRPC, SSH, Postgres, MQTT, even Minecraft… you get the idea.
Connect to services anywhere, no firewall changes required.
Install a lightweight agent to deliver traffic to any service through a secure tunnel.
Run your services in any environment
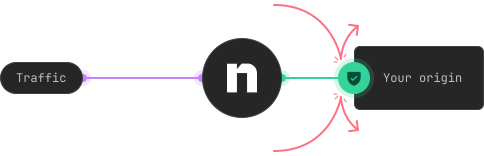
Because your services are connected to ngrok with secure tunnels, they can be deployed anywhere. If it listens on a port and is connected to the internet, ngrok can deliver traffic to it.
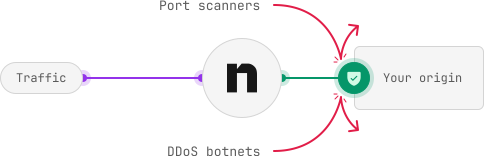
Close every single inbound port
Attackers can’t skirt a secure tunnel to scan or attack your origin servers, which means you whittle down your surface area and remove an entire class of attack vectors.
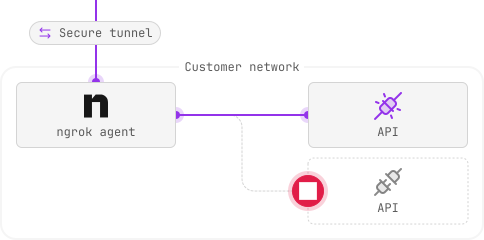
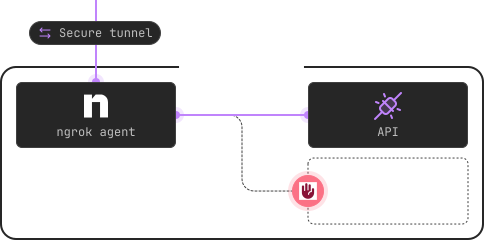
Precise network access, not risky customer VPNs
Drop the ngrok agent into your customers’ networks and tightly scope your access to just the APIs and databases you need. Not their whole subnet.
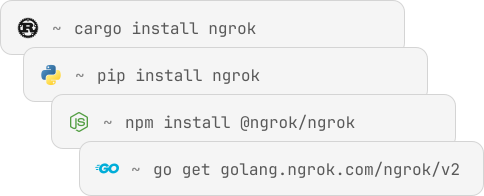
import "ngrok"
Don’t want to package and babysit an agent sidecar? Embed secure tunnels directly into your code with a native agent SDK.
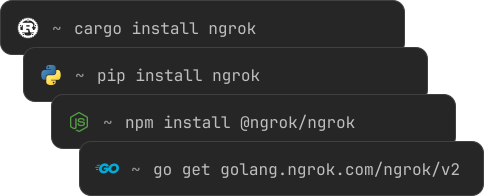
Developer experience matters.
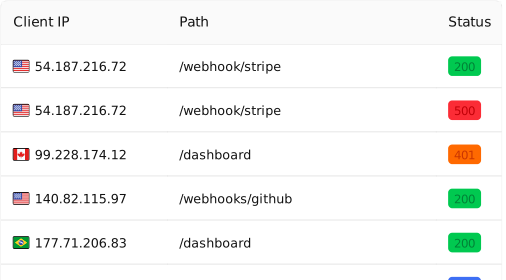
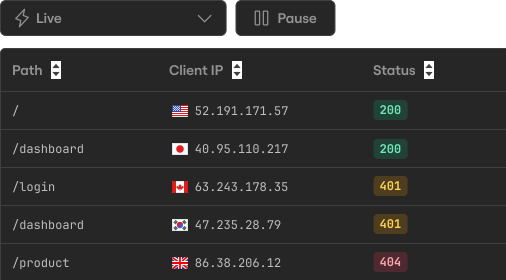
Inspect every detail of your traffic
Watch the flow in real time, then dig into the headers, body, latency, response, and more for every request.
Send traffic logs to your favorite obs platform
Export structured logs to Datadog, Cloudwatch, and Azure Monitor to combine with your existing telemetry.
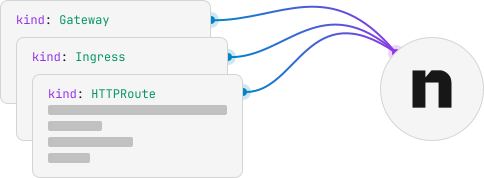
Use your existing Kubernetes manifests
The ngrok Operator slurps up standardized Ingress and Gateway API resources, then transforms them into endpoints and policies that run on our cloud service and deliver traffic to your pods.
Fully programmable
We integrated ngrok into the dev tools you love. There’s an API for every feature to quickly build your own integrations, too. And make them production-ready, declarative, IaC... you get the idea.
All the boxes you need to check
Join millions of developers routing billions of requests every day.
ngrok is so effing amazing
ngrok opened the door for Databricks to rapidly onboard big enterprise customers with comprehensive security much less operational complexity.


I wouldn't know how to work without ngrok.
OMG life changer. I can't imagine how I lived without ngrok.
ngrok has been super user friendly, works seamlessly, and never gets in our way. Today, our engineers spend less time troubleshooting proxy issues and more time building.


Just used ngrok for the first time to show off a new GopherCon web layout. Wow, that's awesome.
ngrok saves me so much time during development. What a tool.
ngrok continues to wow us with great APIs and automation. Establishing secure remote connectivity with our customer's environments via REST APIs is fast and safe ... and amazing!


ngrok makes the hard parts of networking feel effortless.
Gateway questions
Didn't see yours? Ask it below.
Answers come from ngrok.com and the ngrok docs, and can be wrong. Check the linked pages before you rely on one.
You read the whole page. What are you waiting for?
No upfront costs. No contact sales. Pay only for what you use.