Put your local app on a public URL.
Securely expose a web server on localhost to the internet, even from behind a NAT or firewall, with secure tunnels.
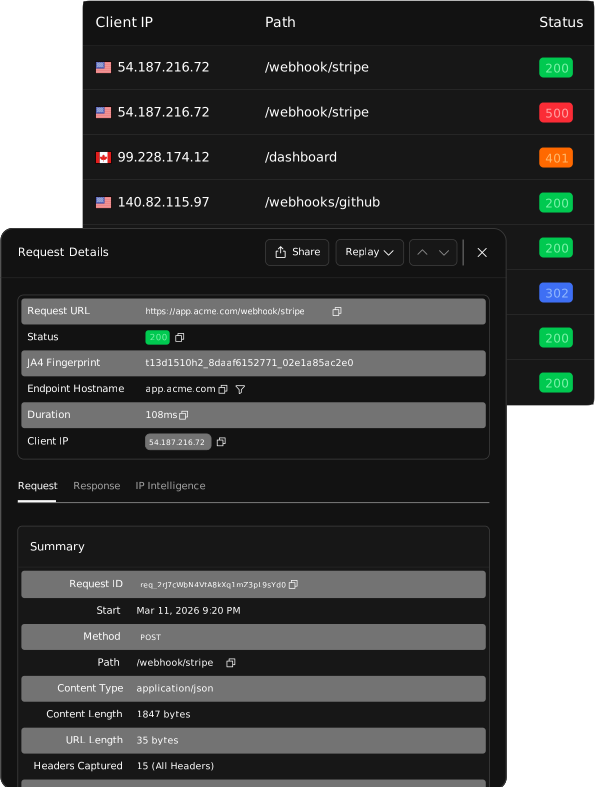
Then, inspect and replay every request in real-time.
Stop context switching and turn “how do I trigger that webhook again?” into a single click to replay.


The fastest way to put anything on the internet.
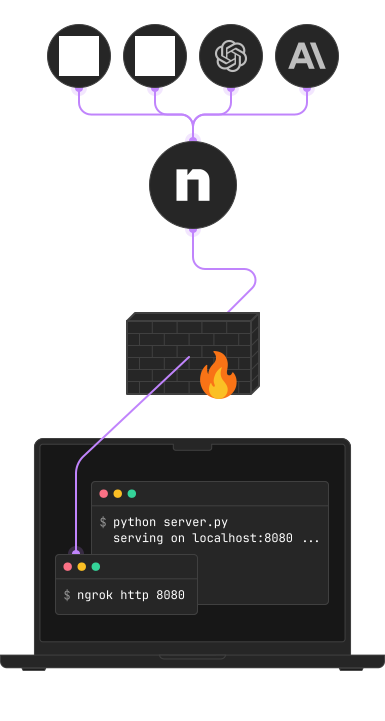
The ngrok agent on your local machine creates a secure outbound tunnel to ngrok's cloud service.
Demo without redeploying
Give your local app a public URL to work with collaborators directly from your dev machine, then protect it with auth.
Build webhook integrations faster
Send webhooks to your local machine to inspect, debug, and iterate. We'll even verify signatures with your signing key.
Connect ChatGPT & Claude to local MCP servers
Let cloud LLMs pull data from your local machine. Debug MCPs with exact request payloads and hit replay to iterate quickly.
Test mobile apps against development backends
Configure your app to use the ngrok URL that points at your local backend—it won’t change between home, work, or a coffee shop.
Get a public URL for your app right now.
ngrok is a standalone executable with zero runtime dependencies that works on every OS.
Install the ngrok agent
Start an endpoint
Open your URL at https://your-assigned-url.ngrok.app
That’s it! You didn’t need to open ports, provision a TLS certificate, or run your own reverse proxy.
Install the ngrok agent
Start an endpoint
Open your URL at https://your-assigned-url.ngrok.app
That’s it! You didn’t need to open ports, provision a TLS certificate, or run your own reverse proxy.
Install the ngrok agent
Start an endpoint
Open your URL at https://your-assigned-url.ngrok.app
That’s it! You didn’t need to open ports, provision a TLS certificate, or run your own reverse proxy.
Install the ngrok agent
Open your URL at https://your-assigned-url.ngrok.app
That’s it! You didn’t need to open ports, provision a TLS certificate, or run your own reverse proxy.
Install the Docker Desktop Extension
Install the Docker Desktop ExtensionFollow the in-app instructions to add your authtoken
Don't have an authtoken? Sign up for a free account.Start an endpoint for a running container
Open your URL at https://your-assigned-url.ngrok.app
That’s it! The extension handles authentication and tunnel setup for you.
Secure your URL with authentication.
Instead of sharing localhost with the whole internet, lock it down to just the people or requests you authorize.
policy.yml
policy.yml
policy.yml
policy.yml
When you're ready for more than just a URL.
Any protocol, not just web services
Developing on databases, Kafka, gRPC, WebSockets, WebRTC, SSH? If it speaks TCP, you can go online in one line.
$ ngrok tcp 22$ ngrok http 80$ ngrok tls 5432Packaged for your stack
The ngrok agent also comes as Docker container, Docker Desktop extension, and Kubernetes Ingress + Gateway controller. Or embed ngrok in your app with native SDKs.
~ docker pull ngrok/ngrok~ npm install @ngrok/ngrok~ helm install ngrok-operator ...Bring your own domain
Create a DNS CNAME record to use your own domain name for your endpoint URL.
Wildcard endpoints
Does your app have multiple subdomains? No problem, handle traffic for all of them with a single command.
Automate with APIs
Automate your dev environment by importing ngrok into your scripts to control it programmatically. See our SDK docs.
Modify traffic, not your app
Add headers, rewrite URLs, redirect paths and replace body text. All without changing your code.
Security and control without slowing down your devs.
- Standardize auth on every endpoint.
- SIEM logging on every request.
- ACL controls on what developers can expose.
So easy it feels like magic.
Get a public URL for localhost in less time than it took you to read this page. Just like 15.3 million other devs.
ngrok is so effing amazing
Spent 3 hours looking for a good ngrok alternative. Let me save you some time: there isn’t a better ngrok alternative.
OMG life changer. I can’t imagine how I lived without ngrok.
PS, it can be this easy in prod too...
No need to “upgrade” to a hodgepodge of ELBs, NLBs, firewall rules, DNS updates, nginx configs, and Cloudflare.
Frequently asked questions
ngrok http 80 and ngrok assigns you a public endpoint, forwarding incoming requests to your local server over an encrypted connection. Skip port forwarding, DNS changes, and firewall rules entirely.ts.net subdomain, a fixed set of ports, no custom domains, and no request inspection or replay. ngrok gives you stable URLs on your own domain, TCP and TLS endpoints, and full traffic inspection. See our ngrok vs. Tailscale comparison for a use-case-by-use-case breakdown.ngrok http 8000 with its port. Paste the resulting URL plus the server's path, such as https://your-assigned-name.ngrok-free.app/mcp, into the client's MCP or connector settings. The dev domain is stable, so the client config survives restarts. Before you share it, put auth in front with Traffic Policy: validate bearer tokens with JWT validation, allow only the AI provider's IP ranges, and rate limit. The inspector at localhost:4040 shows every JSON-RPC request the client sends. Full guide: Using ngrok as your MCP gateway.Answers come from ngrok.com and the ngrok docs, and can be wrong. Check the linked pages before you rely on one.